> For the complete documentation index, see [llms.txt](https://docs.flosum.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.flosum.com/global-settings/security/identity-providers-sso/adding-an-identity-provider-sso.md).

# Adding an Identity Provider (SSO)

{% hint style="success" %}

#### Required User Credentials

\[**Flosum User**] - **SystemAdministrator** Role
{% endhint %}

## ![](https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FSxcnKlaJKPzDqONWoDNv%2FSummary2-Small-Icon.svg?alt=media\&token=5e3253d0-a069-4ba5-9c06-83c70bd0b21d)Overview

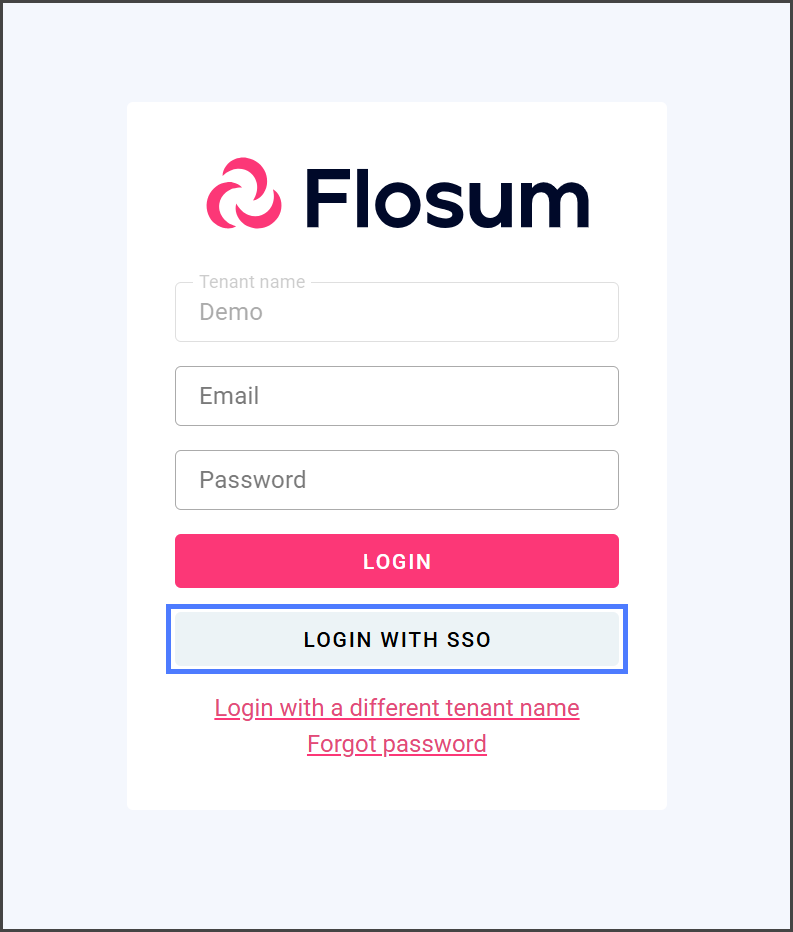
This article explains how to add an Identity Provider to your Flosum tenant to enable Single Sign-On (SSO) for its applications. Once you add an identity provider, a custom SSO button will appear on the login screen. This button redirects users to the identity provider's login page. After they authenticate, they're returned to the Flosum app. For SSO login instructions, see the following article.

* [Logging In With SSO](/global-settings/security/identity-providers-sso/logging-in-with-sso.md)

<div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FFtPs1AdA8osfUhRFE5No%2FAddingAnIdentityProvider-SsoButton_02.png?alt=media&amp;token=b71ed818-1172-446d-8b8a-b06d1a7aa7f4" alt="" width="375"><figcaption></figcaption></figure></div>

### Identity Provider Configuration

{% hint style="info" %}
Flosum Cloud Apps support SSO from an identity provider using either of the following protocols:

* OIDC (OpenID Connect)
* SAML (Security Assertion Markup Language)
  {% endhint %}

This article provides general instructions for configuring your identity provider. Review these before proceeding to the provider-specific articles listed below, which offer instructions and details for the most common identity providers.

**OIDC**

* [Auth0 - OIDC - Configuration](/global-settings/security/identity-providers-sso/oidc-identity-providers/auth0-oidc-configuration.md)
* [AWS Cognito - OIDC - Configuration](/global-settings/security/identity-providers-sso/oidc-identity-providers/aws-cognito-oidc-configuration.md)
* [Microsoft Entra ID - OIDC - Configuration](/global-settings/security/identity-providers-sso/oidc-identity-providers/microsoft-entra-id-oidc-configuration.md)
* [Google IDP - OIDC - Configuration](/global-settings/security/identity-providers-sso/oidc-identity-providers/google-idp-oidc-configuration.md)

**SAML**

* [Microsoft Entra ID - SAML - Configuration](/global-settings/security/identity-providers-sso/saml-identity-providers/microsoft-entra-id-saml-configuration.md)
* [Okta - SAML - Configuration](/global-settings/security/identity-providers-sso/saml-identity-providers/okta-saml-configuration.md)

### Regional URLs

To configure an identity provider for SSO with Flosum Cloud Apps, you'll need the region-specific **Redirect**, **Callback**, and **Sign-Out** URLs. Add the relevant URLs for each app that requires SSO.

**Redirect URLs**

{% tabs %}
{% tab title="United States URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-us.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-us.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>DevOps</td><td>https://devops-us.flosum.app/api/v1/auth/login/open-id</td></tr></tbody></table>
{% endtab %}

{% tab title="Germany URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-de.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-de.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>DevOps</td><td>https://devops-de.flosum.app/api/v1/auth/login/open-id</td></tr></tbody></table>
{% endtab %}

{% tab title="Japan URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-jp.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-jp.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>DevOps</td><td>https://devops-jp.flosum.app/api/v1/auth/login/open-id</td></tr></tbody></table>
{% endtab %}

{% tab title="Australia URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-au.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-au.flosum.app/api/v1/auth/login/open-id</td></tr><tr><td>DevOps</td><td>https://devops-au.flosum.app/api/v1/auth/login/open-id</td></tr></tbody></table>
{% endtab %}
{% endtabs %}

**Callback URLs**

{% tabs %}
{% tab title="United States URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-us.flosum.app/api/v1/oauth/callback</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-us.flosum.app/api/v1/oauth/callback</td></tr><tr><td>DevOps</td><td>https://devops-us.flosum.app/api/v1/oauth/callback</td></tr></tbody></table>
{% endtab %}

{% tab title="Germany URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-de.flosum.app/api/v1/oauth/callback</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-de.flosum.app/api/v1/oauth/callback</td></tr><tr><td>DevOps</td><td>https://devops-de.flosum.app/api/v1/oauth/callback</td></tr></tbody></table>
{% endtab %}

{% tab title="Japan URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-jp.flosum.app/api/v1/oauth/callback</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-jp.flosum.app/api/v1/oauth/callback</td></tr><tr><td>DevOps</td><td>https://devops-jp.flosum.app/api/v1/oauth/callback</td></tr></tbody></table>
{% endtab %}

{% tab title="Australia URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Callback URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-au.flosum.app/api/v1/oauth/callback</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-au.flosum.app/api/v1/oauth/callback</td></tr><tr><td>DevOps</td><td>https://devops-au.flosum.app/api/v1/oauth/callback</td></tr></tbody></table>
{% endtab %}
{% endtabs %}

**Sign-Out URLs**

{% tabs %}
{% tab title="United States URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Sign-Out URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-us.flosum.app/api/v1/oauth/login</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-us.flosum.app/api/v1/oauth/login</td></tr><tr><td>DevOps</td><td>https://devops-us.flosum.app/api/v1/oauth/login</td></tr></tbody></table>
{% endtab %}

{% tab title="Germany URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Sign-Out URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-de.flosum.app/api/v1/oauth/login</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-de.flosum.app/api/v1/oauth/login</td></tr><tr><td>DevOps</td><td>https://devops-de.flosum.app/api/v1/oauth/login</td></tr></tbody></table>
{% endtab %}

{% tab title="Japan URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Sign-Out URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-jp.flosum.app/api/v1/oauth/login</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-jp.flosum.app/api/v1/oauth/login</td></tr><tr><td>DevOps</td><td>https://devops-jp.flosum.app/api/v1/oauth/login</td></tr></tbody></table>
{% endtab %}

{% tab title="Australia URLs" %}

<table><thead><tr><th width="180">Flosum Cloud App</th><th>Sign-Out URL</th></tr></thead><tbody><tr><td>Global Settings</td><td>https://global-au.flosum.app/api/v1/oauth/login</td></tr><tr><td>Backup &#x26; Archive</td><td>https://backup-au.flosum.app/api/v1/oauth/login</td></tr><tr><td>DevOps</td><td>https://devops-au.flosum.app/api/v1/oauth/login</td></tr></tbody></table>
{% endtab %}
{% endtabs %}

## Adding an Identity Provider

{% hint style="info" %}
Global Settings allows you to add multiple providers to your tenant for flexible configurations. For instance, if your organization uses separate identity providers for testing and production, you can add both.
{% endhint %}

{% stepper %}
{% step %}

### Access Global Settings

1. From any **Flosum Cloud App**, click the **App Switcher** icon at the top of the left sidebar menu.

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2Fgh5FcQCnErKAjJ7isiuB%2FGS-Access-01.png?alt=media&amp;token=ddf01506-f133-4e49-825a-76a2a237e3a8" alt="" width="563"><figcaption></figcaption></figure></div>
2. Click **Global Settings**.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2Fx5vntzgpLuT50fMTzwT9%2FGS-Access-02.png?alt=media&amp;token=f67a125f-5087-47c2-9bc6-9393c3d2b7a5" alt="" width="563"><figcaption></figcaption></figure></div>
3. The **Global Settings** app will open in a new tab.

{% hint style="info" %}
Global Settings can also be accessed by logging in directly via the Flosum Cloud Apps Login URL. See the following article for login instructions.

* [Log In To Global Settings](/global-settings/getting-started/log-in-to-global-settings.md)
  {% endhint %}
  {% endstep %}

{% step %}

### Create Identity Provider

1. Click **Identity Providers** from the sidebar menu.
2. Click **Create**.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FZPW5R6oi3ugjlgXaYcQh%2FAddingAnIdentityProvider-S02-01.png?alt=media&amp;token=abb1841b-307f-489f-96b0-2a9f9d531c91" alt="" width="563"><figcaption></figcaption></figure></div>
3. Enter a **Name** for the identity provider.
4. Check/Uncheck **Just-In-Time Provisioning** to enable or disable automatic user creation on SSO login.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FvvjIE6YrUe0K69FS8MHw%2FAddingAnIdentityProvider-S02-02.png?alt=media&amp;token=c02bcaa2-dd50-449c-baac-708769649c6f" alt="" width="563"><figcaption></figcaption></figure></div>

{% hint style="info" %}
The **Just-In-Time Provisioning** feature automatically generates Global Settings user accounts upon the first successful SSO login. See the following article for more details.

* [Configuring Just-In-Time (JIT) Provisioning](/global-settings/security/identity-providers-sso/configuring-just-in-time-jit-provisioning.md)
  {% endhint %}

5. Click the **Type** dropdown menu.&#x20;
6. Select **OPEN\_ID** or **SAML** depending on the type of Identity Provider you are connecting to.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FbBghhYPuKU1QqHiXZsTc%2FAddingAnIdentityProvider-S02-03.png?alt=media&amp;token=8976b62a-9d2a-40a6-a988-5238e39ec7c7" alt="" width="563"><figcaption></figcaption></figure></div>
7. Skip to the relevant step to complete the required fields.
   1. OPEN\_ID: [#enter-openid-information](#enter-openid-information "mention")
   2. SAML: [#enter-saml-information](#enter-saml-information "mention")
      {% endstep %}

{% step %}

### Enter OpenID Connect (OIDC) Information

If you selected **OPEN\_ID**, fill out the fields in the **OpenId Information** section. See the screenshot and table below for more details.

{% hint style="warning" %}
If the Issuer URL is invalid or unreachable, the SSO Button will not appear on the login page.
{% endhint %}

<div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FbKAB6aBkr0RCRZMQ5zMd%2FAddingAnIdentityProvider-S03-01.png?alt=media&amp;token=4177e56d-a395-43fa-a272-fbefbf6d4003" alt="" width="563"><figcaption></figcaption></figure></div>

<table><thead><tr><th width="179.6666259765625">Field</th><th>Description</th></tr></thead><tbody><tr><td><strong>Client ID</strong></td><td>Enter the Client ID of your OIDC application.</td></tr><tr><td><strong>Client Secret</strong></td><td>Enter the Client Secret of your OIDC application.</td></tr><tr><td><strong>Issuer</strong></td><td>Enter the URL of your instance on your OIDC identity provider.</td></tr></tbody></table>
{% endstep %}

{% step %}

### Enter SAML Information

If you selected **SAML**, fill out the fields in the **SAML 2.0 Information** section. See the screenshot and table below for more details.

{% hint style="info" %}
**Optional** fields can be left blank.
{% endhint %}

<div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FrZxF9NJuCDsozynkiZy6%2FAddingAnIdentityProvider-S04-01.png?alt=media&amp;token=57af199a-32ff-485c-8c92-7ba90dc6f0e1" alt="" width="563"><figcaption></figcaption></figure></div>

<table><thead><tr><th width="179.6666259765625">Field</th><th>Description</th></tr></thead><tbody><tr><td><strong>Issuer</strong></td><td>Enter the Identity Provider's ID. This value can be copied from the Identity Provider metadata XML, from the <code>entityID</code> attribute of the <code>EntityDescriptor</code> element.</td></tr><tr><td><strong>Entity ID</strong></td><td>Enter the Service Provider's ID. This can be a string value, but it must match in both the Service Provider and Identity Provider configurations.</td></tr><tr><td><strong>Identity Provider Sign Certificate</strong></td><td>Click to upload the certificate used by the Identity Provider to sign SAML responses and assertions. The Service Provider uses this certificate to verify the authenticity and integrity of received SAML messages.</td></tr><tr><td><strong>Name ID format</strong> (Optional)</td><td><p>This field maps the Identity Provider user to a Global Settings user. Since not all Identity Providers support configuring Name ID Format for SSO login, Global Settings uses the <code>uniqueUserId</code> attribute in the SAML Assertion instead of the Name ID format.</p><p></p><p>Verify your Identity Provider supports Name ID format and enter its value. The standard format is: </p><p><code>urn:oasis:names:tc:SAML:1.1:nameid-format:emailAddress</code></p></td></tr><tr><td><strong>Identity Provider Login URL</strong></td><td>Enter the Identity Provider sign-on (login) URL. This value can be copied from the Identity Provider metadata XML, from the <code>Location</code> attribute of the <code>SingleSignOnService</code> element under <code>IDPSSODescriptor</code>.</td></tr></tbody></table>

#### **SAML Signed Request Enabled**

The **SAML Signed Request Enabled** checkbox indicates whether the authentication request sent by the Service Provider to the Identity Provider is digitally signed. This value can be copied from the Identity Provider metadata XML, from the `WantAuthnRequestsSigned` attribute of the `EntityDescriptor` element under `IDPSSODescriptor`.

If checked, fill out the fields in the following screenshot and table.

<div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FJ6wAc3phiB3A5kfxoviG%2FAddingAnIdentityProvider-S04-02.png?alt=media&amp;token=b542a457-1ee3-42f6-a5fb-6e1f50c986b7" alt="" width="563"><figcaption></figcaption></figure></div>

<table><thead><tr><th width="180.33331298828125">Field</th><th>Description</th></tr></thead><tbody><tr><td><strong>Auth Sign Certificate</strong></td><td>Click to upload the certificate that the Service Provider uses to sign SAML requests. The Identity Provider uses this certificate to verify the authenticity of requests. You must upload this certificate to both the Identity Provider and the Service Provider.</td></tr><tr><td><strong>Auth Private Key</strong></td><td>Click to upload the private key that the Service Provider uses to sign SAML requests. The Identity Provider uses this key to verify the authenticity of requests. This key must match the <strong>Auth Sign Certificate</strong>.</td></tr><tr><td><strong>Auth Private Key Password</strong> (Optional)</td><td>Enter the passphrase used to decrypt the <strong>Auth Private Key</strong> for signing SAML requests. This field can be empty if the private key is not password-protected.</td></tr><tr><td><strong>Auth Sign Algorithm</strong></td><td>Enter the algorithm used to sign SAML requests with the Auth Private Key. Ensure the Identity Provider supports this algorithm. The default is: <code>http://www.w3.org/2001/04/xmldsig-more#rsa-sha256</code>.</td></tr></tbody></table>

#### **Assertion Encryption Enabled**

The **Assertion Encryption Enabled** checkbox enables encryption of SAML assertions by the Identity Provider. When enabled, only the Service Provider with the corresponding private key can decrypt the assertions.

If checked, fill out the fields in the following screenshot and table.

<div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2Fw31DZ1Yx4jWFvTobKfX1%2FAddingAnIdentityProvider-S04-03.png?alt=media&amp;token=cf1fe569-00c1-4fe0-b585-9e6ef3884af8" alt="" width="563"><figcaption></figcaption></figure></div>

<table><thead><tr><th width="180.33331298828125">Field</th><th>Description</th></tr></thead><tbody><tr><td><strong>Encryption Certificate</strong></td><td>Click to upload the certificate used by the Identity Provider to encrypt SAML assertions. This ensures only the Service Provider with the matching private key can decrypt them. You must upload this certificate to both the Identity Provider and the Service Provider.</td></tr><tr><td><strong>Encryption Private Key</strong></td><td>Click to upload the private key that the Service Provider uses to decrypt SAML assertions from the Identity Provider. This key must match the <strong>Encryption Certificate</strong>.</td></tr><tr><td><strong>Encryption Private Key Password</strong> (Optional)</td><td>Enter the passphrase used to decrypt the <strong>Encryption Private Key</strong>. This field can be empty if the private key is not password-protected.</td></tr></tbody></table>

{% hint style="info" %}

#### Certificates and Private Keys

Uploaded certificates and private keys must be properly formatted, ensuring no additional spaces, line breaks, or formatting errors.

* For certificates, include:
  * `-----BEGIN CERTIFICATE-----` and `-----END CERTIFICATE-----`
* For private keys, include:
  * `-----BEGIN PRIVATE KEY-----` and `-----END PRIVATE KEY-----`
    {% endhint %}
    {% endstep %}

{% step %}

### Enter Button and Group Information

{% hint style="warning" %}
You are only required to fill out the **Button Text** field.
{% endhint %}

1. Enter a label for the **SSO Button** on the login page in the **Button Text** textbox.

{% hint style="info" %}
The **SSO Button** appears below the **LOGIN** button on the login page. If you use multiple identity providers, it's helpful to assign different labels to each button to prevent confusion.
{% endhint %}

2. (Optional) Click the **Button Image** textbox to open a file dialog and select an SVG image to display on the login page button.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2F5hqeebVpf1drUrJKkv56%2FAddingAnIdentityProvider-S05-01.png?alt=media&amp;token=d2a6799d-4e70-4e1a-9198-5258167a5df9" alt="" width="563"><figcaption></figcaption></figure></div>

{% hint style="info" %}
For best results, use an SVG image with a height of 24px.
{% endhint %}

3. (Optional) Click the **Group** dropdown menu.
4. (Optional) Select a group to automatically assign users created with this identity provider.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2Fv6oBwbBZeKyN7S4h9Kpl%2FAddingAnIdentityProvider-S05-02.png?alt=media&amp;token=c19f860f-536f-4359-937b-095bd0b0bb1f" alt="" width="563"><figcaption></figcaption></figure></div>

{% endstep %}

{% step %}

### Save Identity Provider

1. Click **Save**.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2Fpp2mYqhU1xK86O1sxZAW%2FAddingAnIdentityProvider-S06-01.png?alt=media&amp;token=b6c9395b-5d28-4c2a-bf47-093fe1985850" alt="" width="563"><figcaption></figcaption></figure></div>
2. You can review the details of the identity provider you set up and preview the SSO Button.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2FT5d4qd43UlhTxxObIwVP%2FAddingAnIdentityProvider-S06-02.png?alt=media&amp;token=38cade58-1c8a-436c-987c-9281a6de617b" alt="" width="563"><figcaption></figcaption></figure></div>
3. Here is an example screenshot of a SAML Identity Provider.&#x20;

   <div align="left"><figure><img src="https://579543750-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2FsEk2hU5IMh3HEY5dJZjR%2Fuploads%2F2hUhB92U0ihcSEawnLAn%2FAddingAnIdentityProvider-S06-03.png?alt=media&amp;token=f9550c4d-0371-4df2-88c9-953c76b05c15" alt="" width="563"><figcaption></figcaption></figure></div>

{% endstep %}
{% endstepper %}


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.

Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:

```
GET https://docs.flosum.com/global-settings/security/identity-providers-sso/adding-an-identity-provider-sso.md?ask=<question>&goal=<user_goal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.
